Grant access through assignment records
A builder can configure Give access on a relation field, selecting the member field, a role scoped to the target record type, and optional start/end date fields. Creating or widening an assignment grant requires permission to share the target record as well as permission to write the assignment. An assignment grants access to its target records, not every record of that type. Use People with access on a record when you have its sharing permission to inspect assignment-derived grants. The scoped role’s Through assignments list shows their source records; change or end the source assignment instead of trying to remove the derived grant there. Date-window changes can take time to refresh; the scheduled boundary check runs every 15 minutes. Removing a derived grant does not remove access supplied by another role or manual share. If access remains, inspect those other grants before broadening permissions. A builder can enable Require permission to export in Access for a record type. Without this setting, export follows list access. With it, members need export permission and exports include only rows within both list and export scopes. Field-read permissions still restrict columns. Test with the intended limited role before distributing a file.Limit a role to matching records
For a role scoped to an organizational unit, location, or position, use the Records filter under each record type in the permissions editor. Choose an available field and one value, then save the role. The filter applies to that record type’s granted verbs for every assignee of the role. It is not a separate filter on each assignee. Other record types in the role keep their own settings. A builder must first enable the field for role rules in the record type’s Access settings. Eligible fields are single-value relation, select, and yes/no fields supported by the editor; text, number, date, multiple-value, and native-column fields are not eligible. The unit scope and field value must both match. Other roles can still grant access, so test the member’s full set of assignments. Review the filter summary before saving, then test a matching record and a nonmatching record as a non-owner. If a field is missing, ask the builder to review its eligibility rather than broadening the role. Check active usage before removing an enabled role-rule field.Goal
Build explainable roles that let Registry, Field Inspection, Decision and Records, and organization administration teams complete their work without expanding access across unrelated Service Centres or records.The access model
Every grant should read as a sentence:This role may perform this verb on this resource in this scope.
The distinction matters. List does not automatically mean open; open does not mean update; update does not mean share or delete. Navigation can be generated for an entity when a member has a useful list or create path, but an entry in the menu is not a promise that every record or action is allowed.
Scope choices and inheritance
Where the selected hierarchy supports it, a role assignment can apply to the exact target, its ancestors, or its descendants.
Do not select an inherited scope merely because it makes a missing record appear. First establish the business boundary; then test a record inside and outside that boundary. Scope is enforced against the record’s applicable scope tokens, not merely as a visual filter.
Design the service roles before opening the editor
Start with a short responsibility map. The following is a starting pattern, not a ready-made permission set:
For each row, list the action that must remain denied. A role is not complete until it has an intended boundary.
Configure a role deliberately
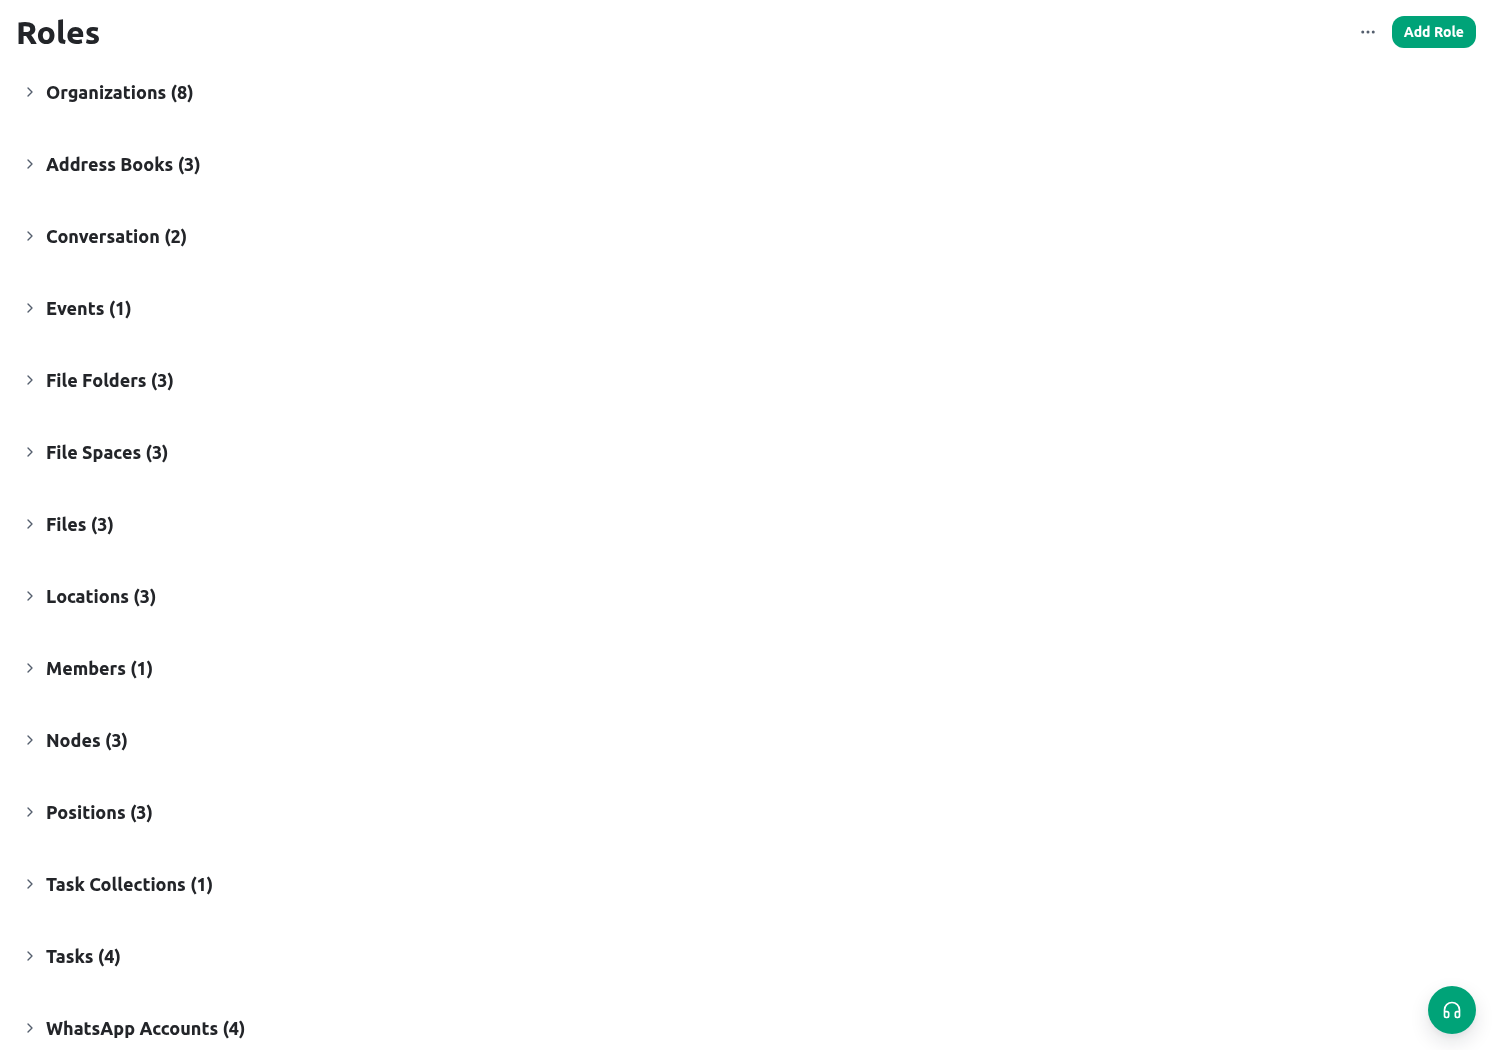
- Open Administration → Roles and scopes and verify that you have the relevant role-management permission. Opening, creating, and updating roles are separate capabilities.
- Choose the role’s administration scope: organization-wide, an eligible hierarchy boundary, a form, or another supported scope. Do not use organization scope as a temporary shortcut.
- Name the role after the responsibility, for example North Service Centre Registry Officer, and describe the business purpose and review owner.
- In the permissions area, select only the resources the role needs. For each resource, select the actual verbs separately.
- Where an assignment permits hierarchy selection, choose Exact, Ancestors, or Descendants intentionally. Record the rationale in the change record.
- Assign the role to the approved member, position, group, or rule-derived recipient. Check whether an inherited assignment from a position or group will also grant it.
- Save one role change at a time. Avoid copying a broad existing administrator role just to resolve one exception.
- Refresh the allowed member context as required and test navigation, list, open, create, update, share/download, and delete actions that matter to the service.
Test the Citizen Service Request boundary
Create two approved non-production requests: one in North Service Centre and one in a different locality. Give each test member only the role being evaluated. Then record the following matrix:
Record the route, member, resource, verb, record scope, expected outcome, actual outcome, and reviewer. A failed negative test is useful evidence: it means the boundary needs correction before publishing, not that the test member needs broader access.
Change control and review
Review a role when a staff member transfers, a position changes, a group changes, a Service Centre moves in the hierarchy, a form becomes published, or a new related entity becomes part of a service. Check both direct and inherited assignments. Before deleting or narrowing a role, inventory its active use. A role change can remove a user’s ability to complete a task, open an evidence file, or access a form that is still part of an active service path. Plan the handoff first; do not use a shared organization-owner account to bridge a gap.Troubleshooting
Related guides
- Manage the people receiving roles in Manage members.
- Learn the everyday access model in Roles and access.
- Use controlled evidence access in Library.
- Diagnose visibility and action failures in Permissions and availability.